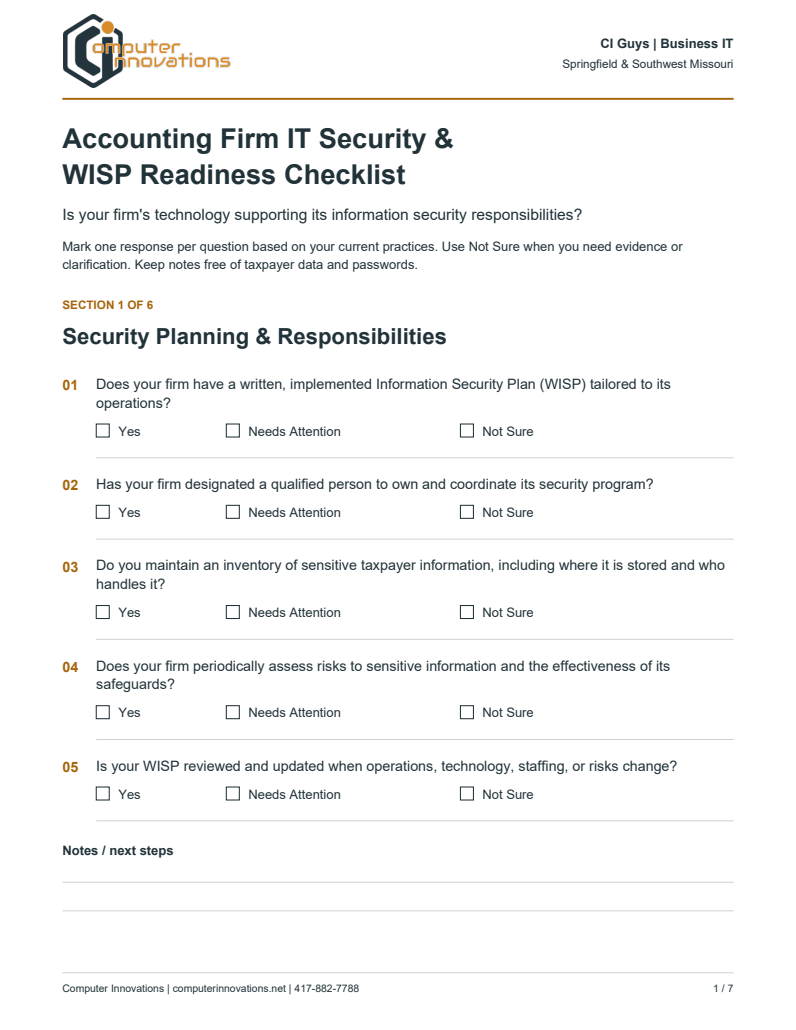
Security Planning & Responsibilities
Security planning, ownership, sensitive information, risk assessments, and keeping your WISP current.
FREE RESOURCE FOR ACCOUNTING & CPA FIRMS
Protecting taxpayer information takes clear responsibilities, informed employees, and technology safeguards that support your firm's written security plan. Start a practical review with our Accounting Firm IT Security & WISP Readiness Checklist.
Download the Free PDF Checklist →30 questions · 7 printable pages · No email address required
SIX AREAS TO REVIEW
Answer Yes, Needs Attention, or Not Sure. The questions help owners and administrators identify what is in place and where a closer look may be useful.
Security planning, ownership, sensitive information, risk assessments, and keeping your WISP current.
Multifactor authentication, individual accounts, appropriate access, offboarding, and password practices.
Updates, endpoint protection, encryption, firewalls, remote access, and vulnerability reviews.
Protection against email threats, recurring education, reporting, and verifying unusual requests.
Backup schedules, protected recovery copies, restoration tests, continuity, and information disposal.
Incident procedures, notification responsibilities, provider oversight, safeguard reviews, and corrective action.
Needs Attention and Not Sure responses may indicate areas warranting further review. Gather the facts, prioritize open questions, and agree who will address each next step. A Yes response is not a compliance finding.
Print the checklist or read it on your device. Keep your completed responses within your firm; you do not need to submit them to access this resource.
Download the Checklist →The CI Guys can help review the technology supporting your security program, from account access and email protection to backup and recovery planning.
IRS guidance emphasizes written security planning for tax professionals. The FTC Safeguards Rule requires covered firms to maintain a written information security program. Your firm's responsibilities depend on its activities and circumstances.
This checklist is an educational self-assessment resource. It is not a complete WISP, legal advice, a formal security assessment, or a determination of regulatory compliance.
Talk with Computer Innovations about the technology supporting your firm's information security responsibilities.
Help improve this site with Google Analytics and masked Microsoft Clarity recordings. Both are optional. Privacy Policy